A penetration test finds and confirms exploitable vulnerabilities in a defined system or application, while a red team exercise simulates a realistic adversary to see whether your people, processes and technology detect and respond to an attack. Choose a pen test when your goal is to find and fix flaws before launch or after a major change. Choose a red team when your detection and response capability is mature enough to be tested, not just your systems. The two are complementary, not interchangeable.
TL;DR:
- Schedule a penetration test before a product launch, after major infrastructure changes, or for compliance, and request proof of exploitation rather than severity scores alone.
- A red team exercise can span several weeks to a few months and should remain hidden from the security operations team to measure real detection.
- Run red team exercises only after a functioning security operations center, consistent patching, and alert review are in place; otherwise, the test may reveal little.
- Use quarterly vulnerability scanning, targeted tests after major changes, and annual or biennial red team exercises once detection and remediation processes are mature.
The fastest way to tell these two assessments apart is to look at what each one is trying to prove. A penetration tester role, as defined by the Canadian Centre for Cyber Security, uses technical methods to identify exploitable vulnerabilities in systems or components, primarily to validate your existing vulnerability management process. A red team goes further: it tests whether your organization notices and reacts to an attacker at all.
Canadian guidance and MITRE both describe red team exercises as an extension of penetration testing, one that layers social engineering and physical elements onto the technical testing to evaluate how an organization actually responds, not just where it is vulnerable.
Penetration testing is a targeted, technical assessment designed to confirm whether specific vulnerabilities can actually be exploited, not just flagged by a scanner. The Canadian Centre for Cyber Security frames it as a method that validates your vulnerability assessment and management processes, which is why it tends to sit downstream of regular vulnerability scanning rather than replacing it.
A typical engagement follows a consistent structure, one that a detailed ecommerce website audit can inform along with NIST SP 800-115 as the standard technical guide for this kind of testing:
The deliverable is a written report your team can act on immediately: a prioritized list of exploitable issues, evidence of exploitation, and clear steps to fix each one. For many organizations, this is also the evidence auditors or clients expect to see before signing off on a vendor relationship.
Pen testing is the right investment before a major product launch, after a significant infrastructure change, or as part of an annual compliance cycle. It answers a narrow, concrete question: can someone break into this system, and how.
Pro Tip: Ask your tester for proof-of-concept evidence, not just a severity score. A report that shows exactly how a vulnerability was exploited is far easier to prioritize than a generic risk rating.
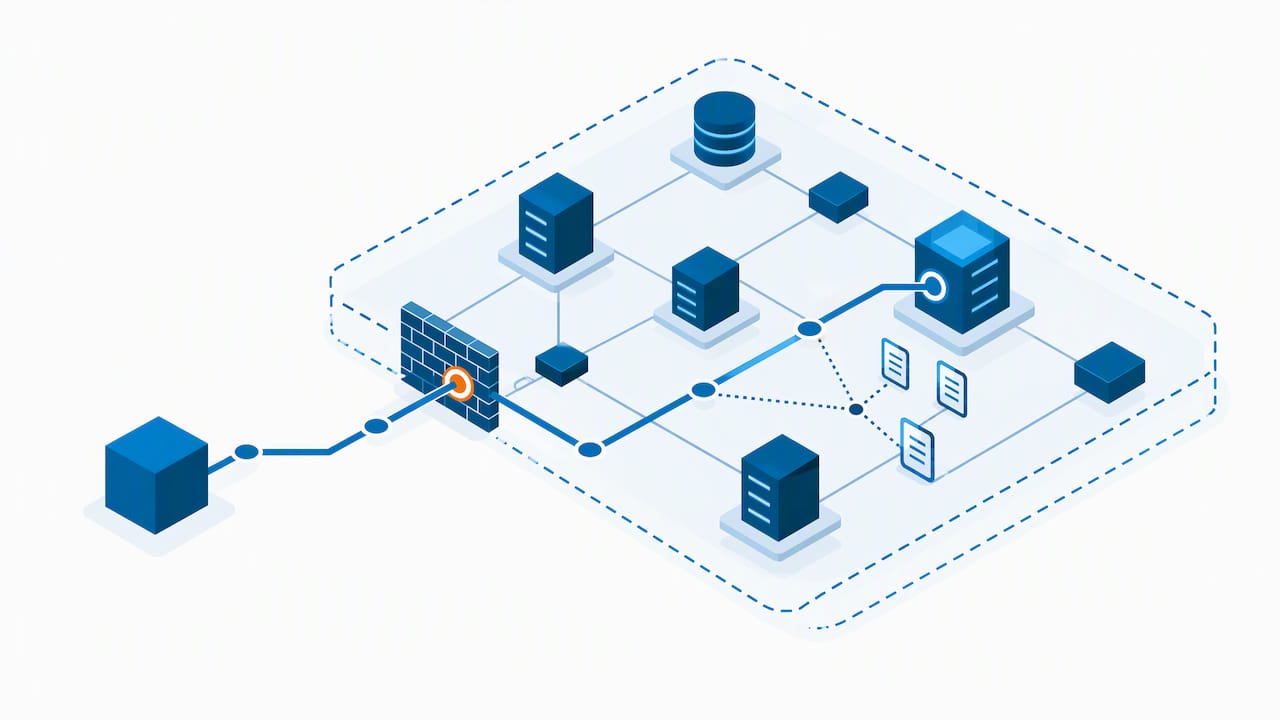
Red teaming simulates a realistic adversary pursuing a specific objective, such as reaching sensitive data or disrupting operations, using whatever combination of technical and human tactics a real attacker might use. It draws heavily on MITRE ATT&CK, the knowledge base that organizes adversary tactics and techniques into a common language red teams use to design emulation scenarios and map results back to detection coverage.
Where a pen test asks “can this be exploited,” a red team asks “would we notice.” The scope is deliberately broad:
A red team exercise is planned around a specific objective and a realistic threat profile, then executed over weeks without the blue team’s foreknowledge, which is what makes the detection results meaningful. The outcome is less a list of bugs and more a timeline: when the attacker got in, how long it took to be noticed, and what happened in between.
This only produces useful results when a few conditions are met. An organization needs a functioning security operations centre capable of generating and reviewing alerts, a reasonably mature patching cadence, and an operator with current knowledge of adversary tactics. Without those, a red team exercise mostly confirms what you likely already suspected: that nobody was watching.
The two assessments diverge most clearly once you look past the definitions and into how each one actually plays out inside an organization.
Two scenarios illustrate the gap. A mid-sized firm runs a pen test on a new client portal before launch and fixes a dozen exploitable flaws, all closed within a month. The same firm later runs a red team exercise and discovers that an attacker who phished a single employee could sit undetected in the network for weeks, because alerts from the endpoint tool were being routed to an inbox nobody monitored. The pen test answered a systems question; the red team answered an operational one.
Timeline and resourcing expectations differ accordingly. A pen test for a typical small or mid-sized environment often runs one to two weeks of active testing with a small team. A red team exercise against the same organization often spans several weeks to a few months once planning, execution and reporting are included, and it typically involves closer coordination with leadership given the broader scope and higher stakes of the simulation. Current Canadian guidance recommends running these kinds of validation activities at a defined frequency, often annually, with prompt remediation of high-impact findings so they do not resurface in the next cycle.
The right choice depends less on preference and more on where your security program actually stands today.
Most organizations are better served starting with pen testing and building toward red teaming once detection capability exists to measure. Running a red team before that capability is in place tends to confirm the obvious rather than reveal anything actionable.
Pro Tip: If you are not sure which assessment fits your current maturity, a short cybersecurity assessment can help clarify where the gaps actually sit before you commit budget to either one.
These two assessments work best as stages in a repeating cycle rather than isolated purchases. A practical 12 to 18 month sequence looks like this:
Each stage feeds the next: pen test findings sharpen detection rules, tabletop exercises confirm the playbook works on paper, and the red team then tests whether it holds up against a real, unannounced attempt. Tracking metrics like time-to-detect and time-to-contain across cycles turns this into a measurable improvement loop rather than a one-off compliance exercise.
A few frameworks consistently anchor credible assessments. MITRE ATT&CK organizes adversary tactics and techniques into emulation plans that red teams use to build repeatable, measurable scenarios, and that defenders use to check their own detection coverage. NIST SP 800-115 sets out the technical methodology behind penetration testing and related validation techniques. Canadian Centre for Cyber Security guidance ties both together, framing red teaming as an extension of penetration testing aimed at evaluating detection, response and business impact.
When vetting a vendor for either assessment, look for:
The most common mistake is not choosing the wrong assessment, it is buying a red team before detection capability exists to measure. Without a working SOC or managed detection in place, a red team mostly confirms silence rather than revealing anything new. Pairing EDR with consistent monitoring first makes every later assessment more useful.
— Geeshan
We run penetration and vulnerability assessments as part of a SOC 2 Type II certified security practice, and we see the same pattern often: organizations ready for a pen test long before they have the detection capability to benefit from a red team. Our 24/7 SOC and MDR service is built to close that gap, so the monitoring, alerting and response processes are actually in place before a red team exercise is worth the spend.
Working with one provider for both sides, the vulnerability testing and the detection infrastructure behind it, means fewer handoffs and a clearer picture of where you actually stand.
If you want help figuring out where your organization sits on that path, our cybersecurity and anti-virus services page is a reasonable place to start.
Red team analysis refers to the review and reporting that follows a red team exercise: how an adversary moved through the environment, what was detected, what was missed, and the business impact of each gap. It focuses on detection and response performance rather than a simple list of technical vulnerabilities.
The red team simulates the attacker, while the blue team is the defending side, the internal or managed security operations function trying to detect and respond to that simulated attack. Purple teaming describes the collaborative middle ground where both sides work together to close gaps faster.
Yes, a penetration tester is a type of ethical hacker: someone authorized to attempt exploitation of systems using the same techniques a malicious actor would use, but under agreed rules of engagement and for the purpose of improving security. Red team operators are also ethical hackers, working under a broader, more adversarial mandate.
A red team exercise is worth the investment mainly for organizations with a functioning SOC and a reasonably mature patching cadence, since the goal is to test detection and response, not just find bugs. For organizations without that foundation yet, a penetration test or a tabletop exercise typically delivers more actionable value first.