NetFusion Designs logo
Heart icon
Support
Email
info@nfd.ca
Phone
647-476-5259(Canada)
IT Services
Icon dropdown arrow

Infrastructure Implementation

Project PlanningHardware Voice over IP (VoIP)Application DevelopmentCloud DesktopSecurity Cameras

Managed IT Services

IT Support24/7 HelpDeskCyber Security & AntivirusData Backups & Disaster
Recovery
Co-Managed ITComplianceEmergency Ransomware
Recovery
Penetration & Vulnerability
Assessment

Optimization of Processes

Microsoft 365 OptimizationVirtual CIO ServicesPenetration TestingInventory Lifecycle
Management
Transforming SMEs with AI
Industries
Icon dropdown arrow
Dental Managed IT Services
Construction
Hotels & Hospitality
Franchises
Financial & Insurance Services
Government
Health Care & PharmaceuticalLegal & Professional Services
Local Small & Medium Businesses
Manufacturing
Non-profit
Real Estate
Retail
Transportation & Logistics
Enterprise & Consulting
Publicly Traded Companies
Our Story
Icon dropdown arrow
About UsTestimonials
Partners
Sponsorship
BlogContact Us
Open menuClose menu
Icon chevron up
Browse Blog:
Business
Insight
Advice
Insight

File Sharing for Multi-Location Teams: A Practical Guide

File Sharing for Multi-Location Teams: A Practical Guide

The best file sharing setup for a team spread across several offices is one managed place for files, tied to your identity system and your device rules, with sharing limits set by policy rather than left to each employee. For most Canadian small and mid-sized businesses, that means SharePoint and OneDrive inside Microsoft 365, configured properly. The tool matters less than the structure, the access rules and the exit plan around it.

This guide walks through how to design that setup, what to lock down, and where multi-location teams usually go wrong.

NetFusion Designs Inc
nfd.ca
Bring Files Together Across Locations
NetFusion Designs manages Microsoft 365 and security for Canadian businesses, helping multi-location teams keep file access and sharing under control.
Explore managed IT services

TL;DR

  • Use one managed repository (for most firms, SharePoint and OneDrive) instead of a file server per office plus email attachments.
  • Tie file access to identity and devices: MFA for everyone, and access only from managed, compliant devices.
  • Set sharing limits centrally: block “Anyone with the link” for sensitive work, restrict external sharing to approved domains, and label confidential files.
  • Organize by metadata and a shallow structure, not by copying each office’s old folder tree.
  • Plan your exit before you sign: you should be able to export your data and have it securely deleted.

Table of Contents

  • Why multi-location file sharing breaks down
  • What a good setup looks like
  • Step 1: Design the structure before you move anything
  • Step 2: Lock down identity with MFA
  • Step 3: Control which devices can open files
  • Step 4: Set sharing rules centrally
  • Extra care for law firms and accounting practices
  • Where your data lives, and how you get out
  • Backup is not the same as sync
  • Our perspective
  • A 30-day plan to get started
  • How NetFusion Designs can help
  • FAQ
  • Sources

Why multi-location file sharing breaks down

Most multi-site businesses did not design their file sharing. It grew. Head office has a file server, the second location mapped a drive over a VPN, a third uses personal cloud accounts, and everyone emails attachments when something is urgent. The result is several copies of the same document, nobody sure which is current, and no clear record of who can open what.

That is called information sprawl. One manufacturing case study describes content scattered across a legacy document system, file servers and several SharePoint sites before it was consolidated. The pattern is common: the problem is rarely a missing tool. It is too many places, with different rules in each.

For teams in different cities, three problems follow:

  1. Version confusion. Two people edit “final_v3” at the same time in Toronto and Winnipeg.
  2. Slow access. Remote offices pull large files across a VPN to a server in another building.
  3. Uncontrolled sharing. A link sent to a client never expires, and nobody can tell who else received it.

What a good setup looks like

A working multi-location file sharing setup has four layers. Skip one and the others carry more risk than they should.

Layer What it does Typical tool in a Microsoft 365 environment
Repository One managed place to store, share, version and recover files SharePoint sites, OneDrive
Identity Proves who is signing in Microsoft Entra ID with MFA
Devices Decides which laptops and phones may open files Intune compliance policies
Data rules Controls what can leave the organization Sensitivity labels, data loss prevention policies

Microsoft’s own file collaboration deployment guidance treats the repository as one part of a wider design that includes identity and device management. A file sharing tool on its own is not a security plan.

SharePoint, OneDrive and Teams: who holds what

This confuses many teams, and the search results show it: people keep asking how Teams and file shares relate. A simple rule works:

  • SharePoint holds files that belong to a team, department, project or location.
  • OneDrive holds an individual’s working files until they are ready to share.
  • Teams is the conversation layer. Files shared in a Teams channel are stored in the SharePoint site behind it.

Once you know that, the design question becomes simple: which SharePoint sites do you need, and who belongs to each?

Step 1: Design the structure before you move anything

The most common mistake is copying every office’s old folder tree into the cloud. You end up with ten levels of folders, paths that hit length limits, and the same confusion you had before, now online.

A better approach:

  • Make sites by function or client group, not by city. “Finance” and “Operations” age better than “Kitchener Office Files”, because people move and offices open or close.
  • Keep folders shallow. Two or three levels is usually enough.
  • Use metadata. Tag files by customer, project, document type or status so people find them by search and filter. The case study mentioned above shows how classification, not folder depth, helped reduce friction across scattered content.
  • Agree on naming conventions and write them on one page. Consistent names matter more than perfect ones.
  • Name an owner for each site. Someone approves access and reviews it each quarter.

A worked example: a manufacturer with plants in two cities and a head office keeps quality documents, customer drawings and HR records. Instead of three folder trees, it builds a Quality site, an Engineering site with a customer tag, and a restricted HR site. Plant staff see the first two. Only HR sees the third. Each site has one owner.

Step 2: Lock down identity with MFA

When files live in the cloud, the sign-in is the front door. Multi-factor authentication (MFA) asks for a second proof, such as an app approval, so a stolen password alone is not enough.

The Government of Canada’s Security Playbook for Microsoft 365 is written for federal departments, but it is a useful public benchmark. It treats MFA and data loss prevention as core controls for SharePoint and OneDrive. The Canadian Centre for Cyber Security’s baseline controls for small and medium organizations add the principle of least privilege: people get only the access they need for their tasks, and administrator accounts are restricted further.

Practical points for rollout:

  • Enforce MFA for every user, not just administrators and not just remote staff.
  • Prefer app-based approval or hardware keys over text messages where you can. If you want a physical option, hardware security keys for protecting Azure accounts are one route, though the page is in Bulgarian.
  • Keep two emergency admin accounts that are excluded from normal policies and monitored closely.
  • Roll out in waves, with a short guide for staff, so the helpdesk is not flooded on day one.

We cover the rollout in detail in our post on MFA for Microsoft 365, and on how to apply rules by location, device and risk in conditional access policies.

Step 3: Control which devices can open files

Multi-location teams mix office desktops, home laptops and personal phones. If any device can sync a SharePoint library, a lost laptop in one office becomes a data incident for the whole company.

The usual answer is to combine identity with device management: files open only from devices that are enrolled, encrypted and up to date. Microsoft’s guidance describes this pairing of Entra ID and Intune with SharePoint. In practice:

  • Enrol company laptops and phones in Intune.
  • Require disk encryption, a screen lock and current updates for access.
  • Allow browser-only access, with downloads blocked, from unmanaged personal devices.
  • Be able to wipe company data from a lost device without touching personal photos.

Our Intune device management setup guide walks through the steps, and the Microsoft 365 security baseline post explains how to tighten settings without breaking the applications your staff rely on.

Step 4: Set sharing rules centrally

Internal sharing is the easy part. The risk sits at the edge, where files go to clients, suppliers and contractors.

In the SharePoint admin center you set an organization-wide sharing level, and you can make individual sites stricter. Microsoft documents these sharing settings for SharePoint and OneDrive, including how guest accounts work through Microsoft Entra B2B. A sensible baseline for most firms:

  • Turn off “Anyone with the link” for anything but genuinely public material. Anonymous links cannot be traced to a person.
  • Require named recipients who verify with a one-time code or a guest account.
  • Use domain allow lists so external sharing works only with approved partner organizations. The Government of Canada playbook cited above recommends this kind of restriction, along with preventing guests from resharing content they do not own.
  • Set link expiry so access ends on its own.
  • Review guests every quarter and remove those you no longer work with.

Sensitivity labels and data loss prevention

Rules that depend on staff remembering are weak. Labels and data loss prevention (DLP) enforce policy automatically. A file marked “Confidential” can be blocked from external sharing even if someone picks the wrong link type. Microsoft explains how to create a DLP policy for SharePoint and OneDrive that stops sensitive items being shared with outside users. Check which Microsoft 365 licence includes the features you need before you plan around them, since some are not in the entry-level plans.

This fits the PIPEDA safeguards principle, which expects protection to include organizational measures such as limiting access on a need-to-know basis, as the Privacy Commissioner’s safeguards bulletin describes.

Extra care for law firms and accounting practices

If you handle client confidences, email attachments are the weak point. LawPRO’s practice risk material on client portals notes that standalone file sharing services and Microsoft 365 can provide many client portal functions. A portal-style library gives each client a private space, an audit trail and no loose attachments.

For firms with offices in several cities, a few additions help:

  • One client-matter structure across all offices, so a lawyer or accountant in Mississauga finds a file the same way as a colleague in Montréal.
  • Matter-level permissions, with ethical walls where a conflict requires them.
  • Evidence that your controls work. Keep MFA reports and backup test logs, because insurers and regulators increasingly want proof rather than a statement that controls exist.

See our guides on SharePoint for law firms, cloud solutions for law and accounting firms and cloud backup for accounting firms.

Where your data lives, and how you get out

Many Canadian owners ask first about server location. It matters, but it is only part of the picture. The Privacy Commissioner’s guidance on cloud computing for small and medium-sized enterprises says that private-sector privacy law does not prohibit transferring personal information to another jurisdiction, but you remain accountable and must understand how the law applies. The Canadian Bar Association’s cloud computing toolkit asks the same questions: where is data stored, what risks come with that jurisdiction, and can foreign entities access it?

Before you commit to a platform, get written answers to these:

  1. Where is our data stored, and can we require Canadian residency?
  2. Does the provider use our data for any secondary purpose, such as training AI, and is that off by default?
  3. Who at the provider can access our content, and is it logged?
  4. How do we export everything, in what format, and how fast?
  5. Does the provider securely delete our data when we leave, and will they confirm it in writing?

Question four and five are your exit strategy. Skipping them is how businesses end up locked in. Our post on why Canadian data sovereignty matters goes deeper on residency.

Backup is not the same as sync

SharePoint versioning and the recycle bin protect against many mistakes, but a synced library is not a backup. A deletion, a ransomware encryption or a malicious insider can propagate across every office within minutes. Keep an independent, tested backup of your Microsoft 365 data and write down your recovery targets. Our guides on disaster recovery plan steps and why you need a disaster recovery plan cover the basics.
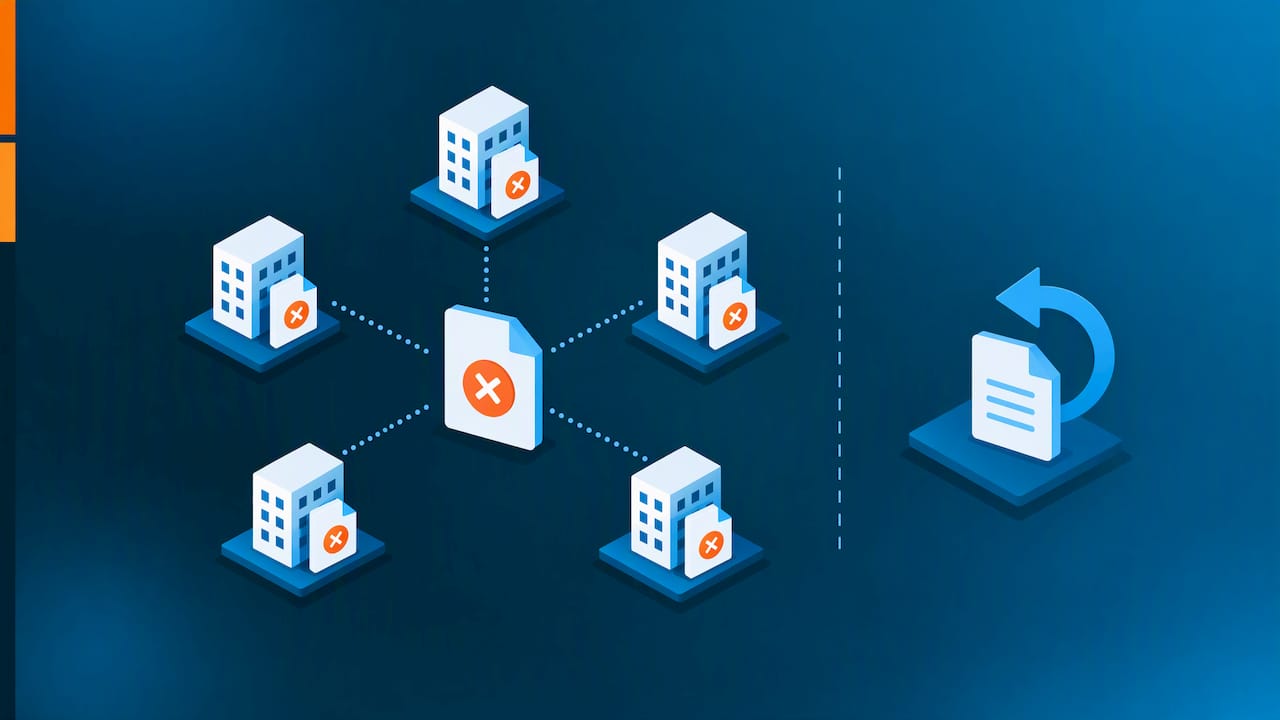
Sync propagation contrasted with separate file backup

Our perspective

We see the same pattern with multi-location clients. They arrive asking which file sharing product to buy. The better question is who is responsible for the rules around it.

A tool with no owner drifts. Guests pile up, links stay open, new hires get copied permissions from someone who left, and each office quietly builds its own workaround. In our experience, the firms that stay secure are not the ones with the most expensive licences. They are the ones where identity, devices, sharing policy and backup are managed as one system, and reviewed on a schedule.

That is why we run these as a single service. Our team manages the Microsoft 365 tenant, the devices, the monitoring and the helpdesk together, with a 24/7 NOC and SOC 2 Type II certification behind it, so there are no third-party vendors for you to coordinate. We also explain each setting in plain language, so your leadership knows what the controls do and why. When a client needs data kept in Canada, we plan for it from the start rather than as an afterthought.

Our advice: start smaller than you think. Pick one function, such as finance or quality, build the structure, apply the policies, and move it. Then repeat. A phased migration with clear ownership beats a weekend big bang.

— Geeshan

A 30-day plan to get started

  1. Week 1: inventory. List every place files live: servers, cloud accounts, shared drives, and who uses them. Note what is sensitive.
  2. Week 2: design. Define sites, owners, naming rules and the sharing baseline. Confirm licensing.
  3. Week 3: secure. Enforce MFA, enrol devices, switch on sharing limits and labels.
  4. Week 4: pilot. Migrate one team, train them for an hour, collect feedback, and adjust before moving the next.

Expect the full migration for several locations to take longer than 30 days. The point of the first month is to have the rules right before the volume arrives.

How NetFusion Designs can help

If you would rather not build this alone, our Microsoft 365 optimization work covers migration, SharePoint structure, security settings and user training. For ongoing care across all your locations, our managed IT services bring helpdesk, monitoring, security and backup under one agreement, with predictable monthly pricing. If you already have an in-house IT person, our co-managed IT option can cover the gaps. We have teams in Kitchener-Waterloo, Toronto, Markham, Mississauga, Montréal and Winnipeg.

FAQ

What is the best file sharing tool for a team in several offices?

For most Canadian small and mid-sized businesses already using Microsoft 365, SharePoint with OneDrive is the practical choice, because it adds no new vendor and works with your identity and device controls. The better choice is the one you can govern: with clear owners, MFA and sharing limits. Very specialized needs, such as heavy engineering files, may call for added tooling.

Can we keep our old file server?

Yes, many firms run a hybrid setup for a while, especially when large files or legacy applications depend on it. The risk is that two systems mean two sets of rules. Treat a hybrid as a transition with an end date, and apply the same MFA and access reviews to both.

Is “Anyone with the link” sharing safe?

Not for sensitive work. Anonymous links cannot be tied to a person and can be forwarded. For client, financial or legal files, use named recipients, expiry dates and sensitivity labels that block external sharing.

Does data have to stay in Canada?

Private-sector privacy law does not, in general, prohibit transferring personal information to another jurisdiction, according to the Privacy Commissioner’s guidance, but you stay accountable for it. Some contracts, clients or sector rules require Canadian residency, so check yours before choosing a platform.
Sources

  • Security Playbook for Microsoft 365, Canada.ca
  • Baseline cyber security controls for small and medium organizations, Canadian Centre for Cyber Security
  • Deploy file collaboration, Microsoft Learn
  • Manage sharing settings for SharePoint and OneDrive, Microsoft Learn
  • Create a DLP policy for SharePoint and OneDrive, Microsoft Learn
  • How P38, Inc. reduced operational friction, M-Files
  • PIPEDA interpretation bulletin: Safeguards, Office of the Privacy Commissioner of Canada
  • Cloud computing for small and medium-sized enterprises, Office of the Privacy Commissioner of Canada
  • What is cloud computing, Canadian Bar Association
  • Client portals, LAWPRO Magazine, March 2024
  • Mandatory MFA for Azure accounts, Smartmanagement.bg

Recommended

  • Multi-Site Network Design for SMB
  • Citrix vs RDS vs ZTNA: How Should Staff Reach Work?
  • Co-Managed vs Fully Managed IT: Where’s the Line?

Continue Reading

Construction Site Internet: How to Connect a Job Site Trailer
Switching IT Providers in Toronto: A Safe Handover Plan
Hybrid Cloud for SMBs: A Practical Guide for Canadian Firms
Microsoft 365: Validate Migration Steps Before Cutover for IT Teams
NetFusion Designs logo
NetFusion Designs is a globally recognized IT service provider and services clients across North America.

We hold a SOC 2 Type 2 report, and maintain internal processes and procedures that keep our clients’ data secure and confidential.
NetFusion Designs IT support team

IT Services Near Me

BurlingtonOakvilleHamiltonMississaugaMiltonBramptonEtobicokeBrantfordGuelphKitchenerWaterlooCambridgeSt CatharinesTorontoMarkhamCaledonNewmarketNorth YorkPickering & DurhamLondonMontreal

Services

Project PlanningHardwareTelephony & VoIPApplication DevelopmentCloud DesktopSecurity CamerasHelpdesk & SupportCyber Security & Anti-VirusData Backups & Disaster RecoveryMicrosoft 365 OptimizationVirtual CIO ServicesPenetration TestingPricingSchedule a MeetingRemote Support
Pricing

Pages

Free Security ScanAbout UsOur Migration ApproachWork CultureOur Core ValuesCode of ConductTestimonialsContactBlogSchedule a MeetingRemote Support

TORONTO

Bank capital office building law
401 Bay St, 16th Floor, Toronto Ontario
Email
info@nfd.ca
Phone
647-476-5259 (Canada)

MARKHAM

Bank capital office building law
141 Main Street N, Markham, ON L3P 1Y2
Email
info@nfd.ca
Phone
647-476-5259 (Canada)

TRI-CITY AREA
(Kitchener / Waterloo / Cambridge)

Bank capital office building law
22 Frederick St, Suite 700, Kitchener Ontario
Email
info@nfd.ca
Phone
647-476-5259 (Canada)

PEEL REGION

Bank capital office building law
6700 Century Ave, 3rd floor, Mississauga, ON L5N 1V8
Email
info@nfd.ca
Phone
647-476-5259 (Canada)

DURHAM REGION

Bank capital office building law
1315 Pickering Parkway, Pickering, ON L1V 7G5
Email
info@nfd.ca

MONTREAL

Bank capital office building law
8815 Av du Parc #402, Montréal, QC H2N 1Y7
Email
info@nfd.ca
Phone
647-476-5259 (Canada)

Special Offers

Radio station signal antena tower
Pricing: $100–185 per user
Icon chevron right
Terms and ConditionsPrivacy PolicyCookie Policy
© 2026 NetFusion Designs Inc.
LinkedInFacebookAlignable logo